“How to Download GTA6” May Be the Riskiest Search of the Year
Have you noticed an unusually high number of time-off requests for November 19th?
The launch of GTA 6 is a global entertainment event 12 years in the making, and is drawing attention far beyond gaming. Trailers, mainstream headlines, social feeds, and fan speculation have turned the countdown into a worldwide conversation.
After years of anticipation, the urge to get back to Vice City first is powerful, and that is exactly the feeling threat actors hope to exploit.
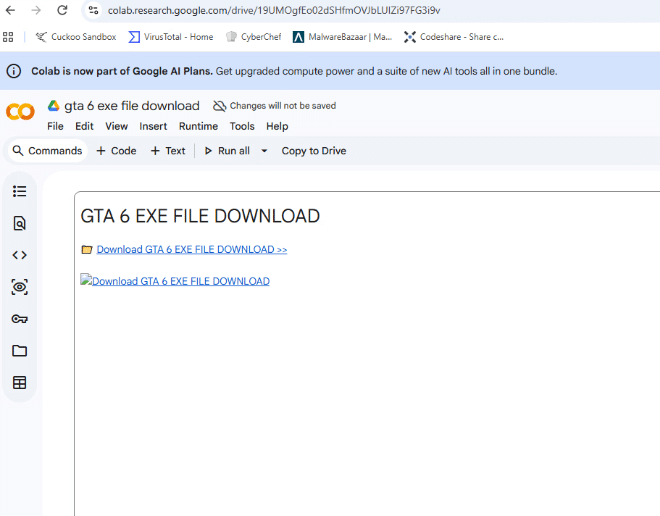
Searches for “GTA 6 free download” or “GTA 6 PC download” can lead to convincing offers. A page promising “early access,” a “leaked build,” or a “free PC installer” borrows the excitement around the real release to make a risky click feel like an opportunity. Add familiar artwork, a prominent download button, and a few reassuring security badges, and the promise can look convincing briefly. Before you follow it, let’s see how these scams play out with a real example, from the first lure to the executable and the alerts it triggered in Cynet.
The Lure: How to Install GTA6
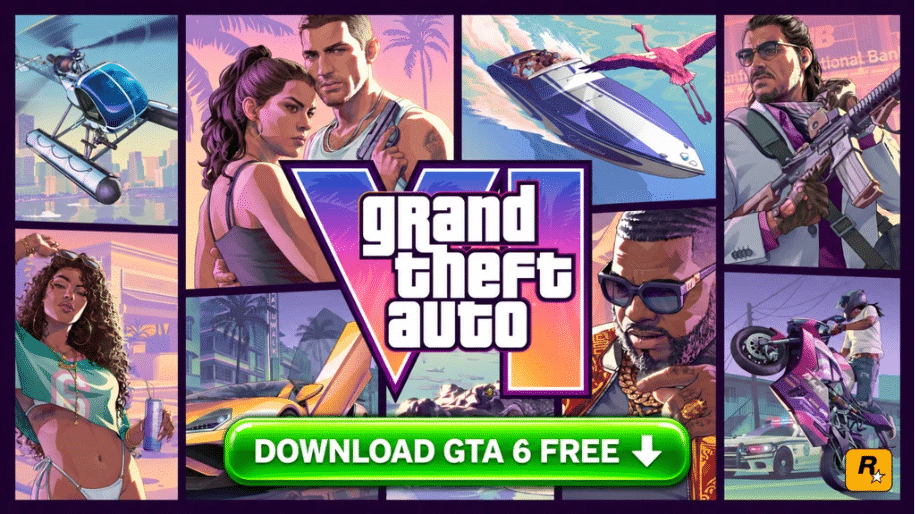
It starts with a simple promise: “GTA 6 EXE FILE DOWNLOAD.” This fake GTA 6 installer lure matches the kind of “GTA 6 EXE file download” promise a player might search for. The Colab notebook below places that phrase above a download link. A familiar hosting platform can make the page feel credible, but it does not establish who supplied the file or whether it is safe. In the team’s reported sequence, this lure leads to the download page shown next.
The next page works harder to win your trust. “Windows Software Hub” presents the download as ordinary Windows software, complete with a version number, a download count, and “Virus Free,” “Secure,” and “Verified” badges. Its claim of “0 threats detected” is part of the pitch. None of those statements verify the file’s safety.
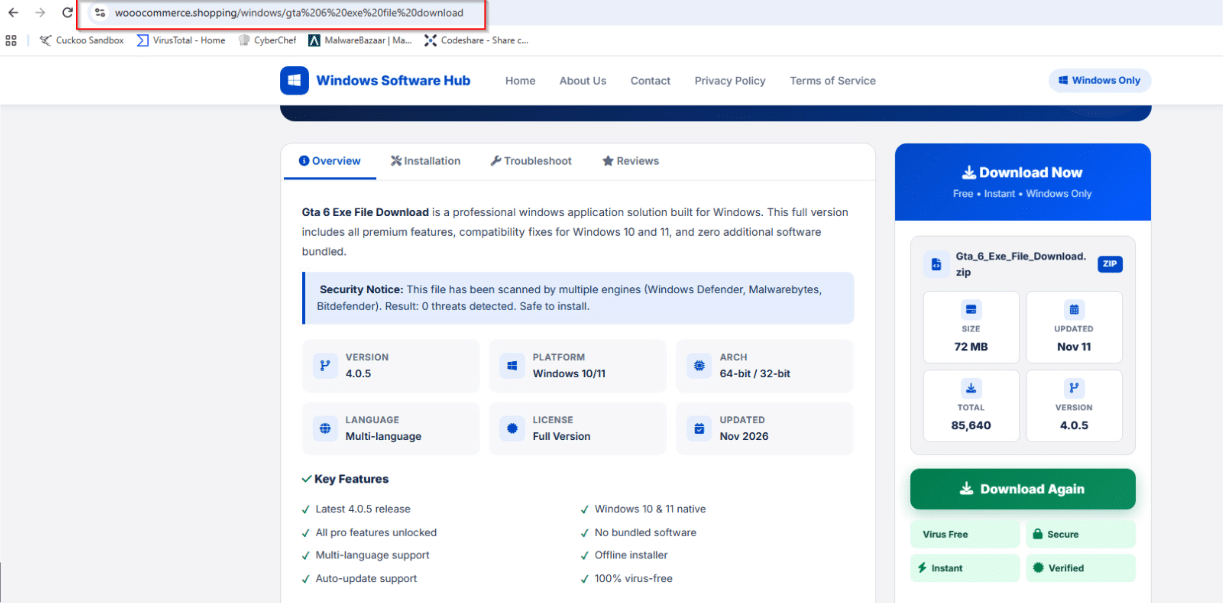
How To Run GTA6 on PC
Any site promising a download for PC is already highly suspect, if not fully malicious, as there is no PC version of the game included in the November 19 release.
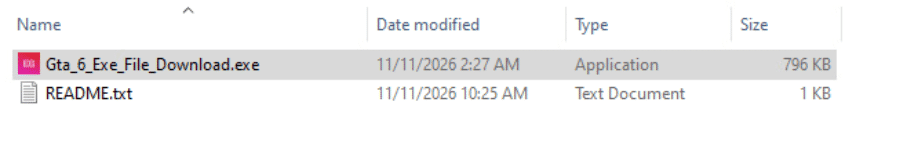
In our example, the download produces Gta_6_Exe_File_Download.zip. This supposed GTA 6 download for Windows arrives as a ZIP containing an EXE file. Opening the archive reveals an executable and a README, not evidence of a genuine game build. Explorer lists the executable at just 796 KB; the landing page advertised a 72 MB download. Those are different measurements, and neither proves that the package contains GTA 6.
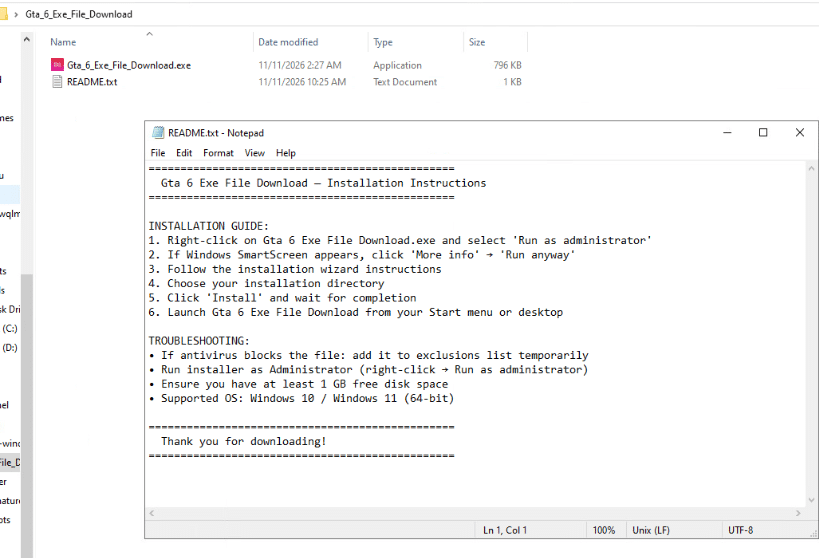
The README is where persuasion becomes explicit. It tells the reader to run the executable as administrator, bypass a security warning, and add an antivirus exclusion if the file is blocked. The page first asks for trust; the instructions then ask the user to weaken the protections that could challenge it.
Congratulations! Your information has been stolen
This file is not GTA 6 – it is a heavily obfuscated WARDEN Stealer loader disguised as a game lure. It evades virtual machines and sandboxes, injects code into browser processes, steals passwords, cookies, browsing data, browser-extension secrets, Steam and Roblox credentials, and cryptocurrency-wallet information. It also replaces copied cryptocurrency addresses and can download additional malware.
The “GTA 6” identity is only social engineering: the binary contains no game engine, assets, Rockstar signatures, or legitimate GTA functionality. Instead, it contains encrypted payloads, credential-theft logic, process injection, clipboard hijacking, and communication with the probable C2 domain uroker[.]casa.
How Cynet Detects and Blocks Threats from Vice City and Beyond
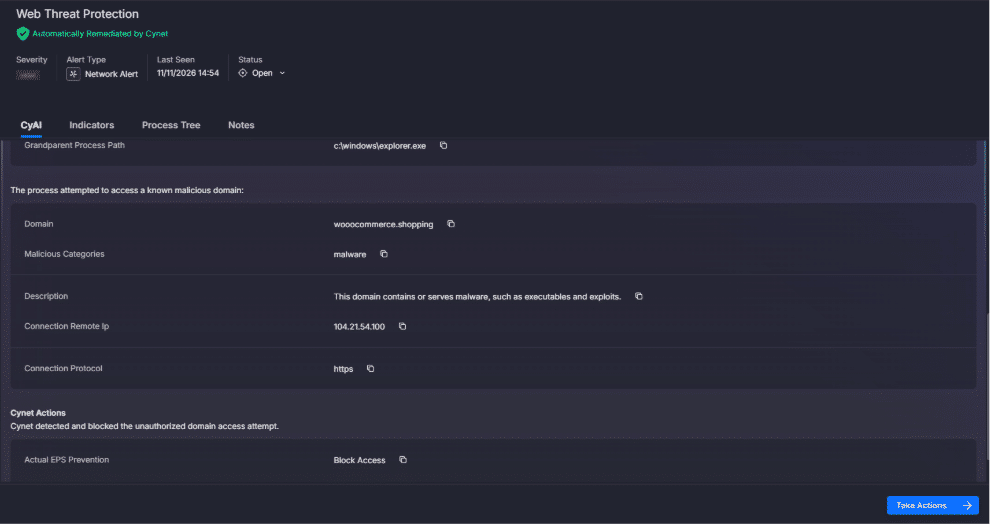
What looks like a convincing download page to a users is an easily recognizable threat for Cynet. When a process attempted to connect to wooocommerce[.]shopping, Cynet’s DomainFiltering identified the destination as a known malware-serving domain and automatically blocked access. The Web Threat Protection alert recorded the attempt and confirmed “Block Access”, interrupting the connection to the malicious site behind the fake GTA6 download.
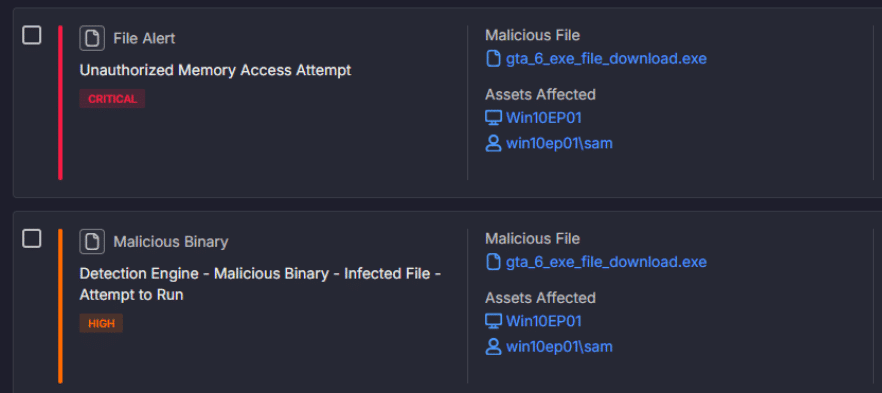
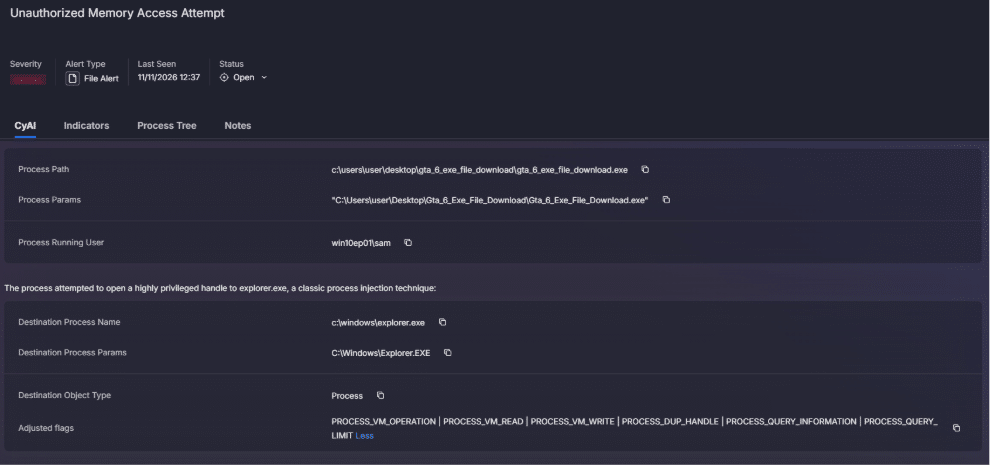
In the test, Cynet detected and blocked gta_6_exe_file_download.exe. Since we let it run in our testing environment, the fake GTA 6 download delivered malware, not a playable game. The activity triggered a High-severity malicious-binary “Attempt to Run” alert and a Critical “Unauthorized Memory Access Attempt” alert.
The alert details connect the detection to the executable inside the extracted download folder, showing its path and running-user context. This gives the security team a clear starting point for investigating the attempted execution.
The confirmed test outcome: Cynet detected and blocked the threat. The alerts shown here document the malicious-binary and memory-access detections associated with that test.
Conclusion
The next big release, whether it comes from Rockstar, Bethesda, or Blizzard, will bring another wave of excitement, and another opportunity for attackers to turn curiosity into a click. Your protection should not depend on spotting every convincing fake – or relying on a single analyst who took the launch day off.
In this test, Cynet detected and blocked the threat behind the scam. We’re here to help protect your organization when the next tempting campaign shows up.
Indicators of Compromise
| Type | Indicator | Confidence | Notes |
| SHA-256 | 6444a4e18c9ca99b5516e5365baac88bf4d62182e3630451b202c9bfb4ccbc0b | High | Original malicious EXE |
| SHA-256 | d56abdfd6b0f00059bace02d168ed9d053621aa809325f112069d23f192f8b35 | High | README distributed with sample |
| Domain | uroker[.]casa | High | WARDEN Stealer C2 |
| URL | hxxps://uroker[.]casa/ | High | WinHTTP POST endpoint |
| IPv4 | 104.21.75[.]176 | Low | Shared Cloudflare address; do not block independently |